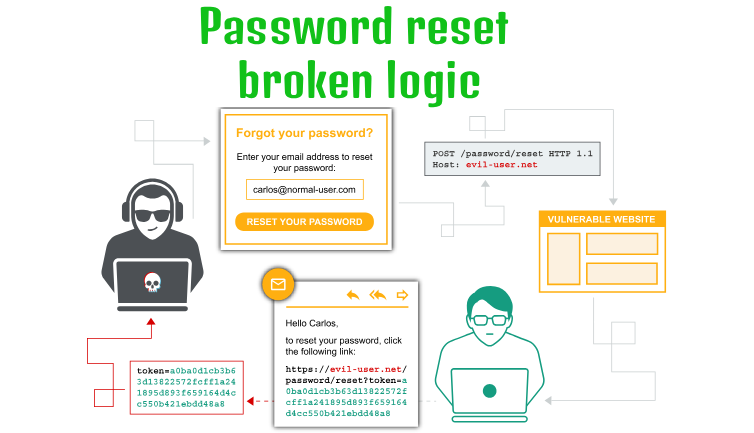
Password reset broken logic - PortSwigger
Exploiting broken password reset logic by reusing a reset token and bypassing token validation to reset another user's password.
Exploiting broken password reset logic by reusing a reset token and bypassing token validation to reset another user's password.
Exploit a stored XSS vulnerability to steal a user's stay-logged-in cookie, crack its MD5 password hash offline, and gain unauthorized account access.
Learn how to bypass weak two-factor authentication by brute-forcing a four-digit MFA code with Burp Suite Intruder, session handling rules, and macros.
Learn how to exploit a weak stay-logged-in cookie implementation by decoding its Base64 structure, cracking an MD5 password hash, and brute-forcing a valid authentication cookie.
Learn how flawed 2FA verification logic can allow an attacker to change the target account and bypass authentication by brute-forcing a four-digit MFA code.
Learn how improper enforcement of two-factor authentication allows an attacker to bypass the verification step and access another user's account by manipulating an account identifier.
Exploit a JSON array injection weakness to submit multiple password candidates in a single login request and bypass request-based brute-force protection.
Enumerating valid usernames by exploiting account lockout behavior, then identifying a valid password using Burp Suite Intruder and Grep-Match.
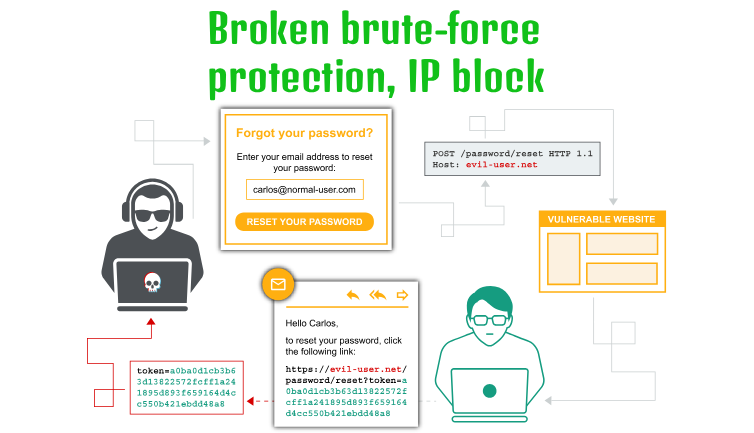
Bypassing flawed IP-based brute-force protection by alternating authentication requests and automating login sequences with Burp Suite Intruder and Macros.
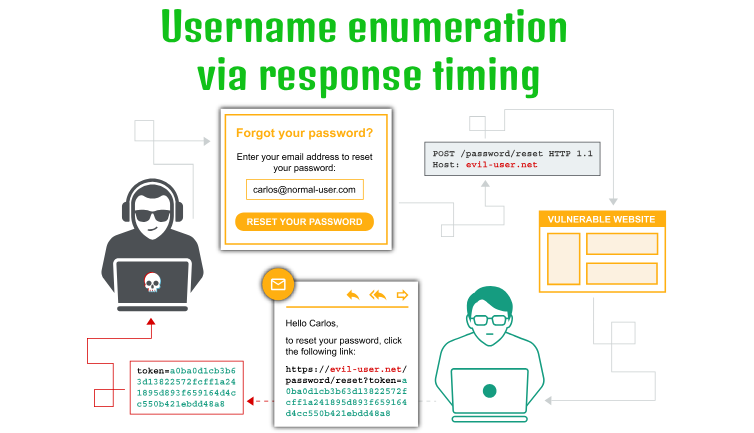
Exploiting response-time differences to enumerate valid usernames and passwords using Burp Suite Repeater, Intruder, and the X-Forwarded-For header.