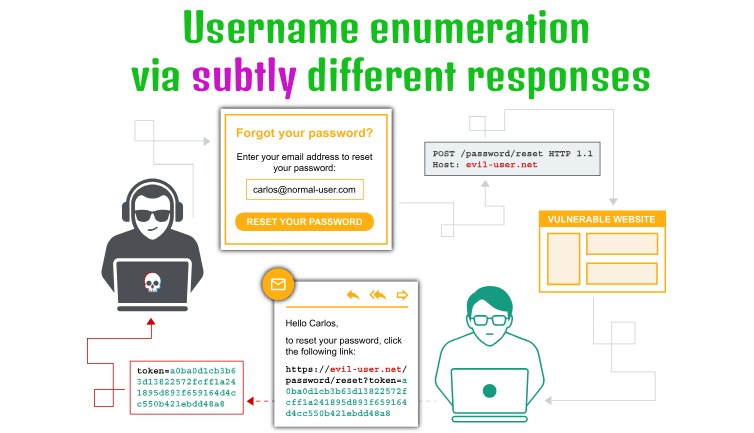
Username Enumeration via Subtly Different Responses - PortSwigger
Exploiting subtle differences in login error messages using Burp Suite Intruder to enumerate a valid username and password.
Exploiting subtle differences in login error messages using Burp Suite Intruder to enumerate a valid username and password.
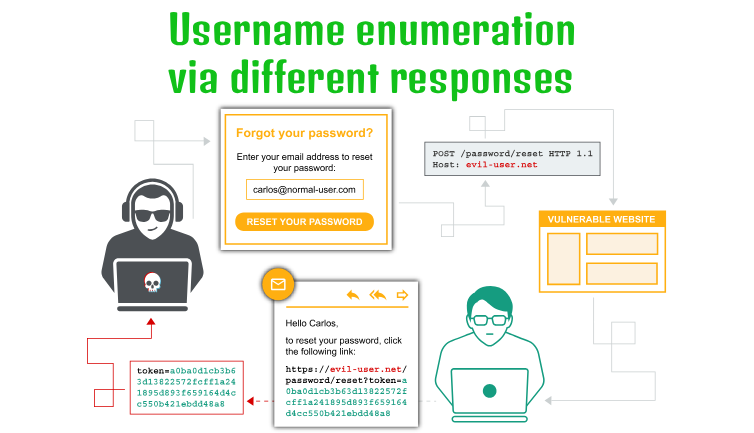
Using Burp Suite Intruder to enumerate valid usernames and identify a valid password by analyzing differences in application responses.
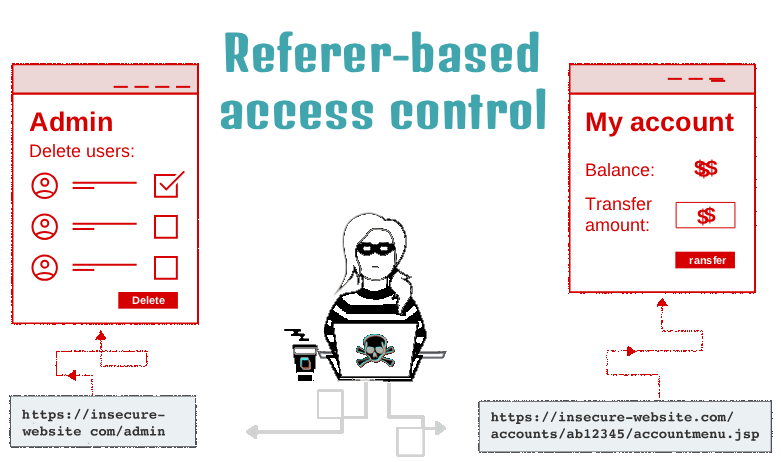
Exploiting a Referer-based access control weakness to bypass administrative authorization and escalate a standard user's privileges using Burp Suite.
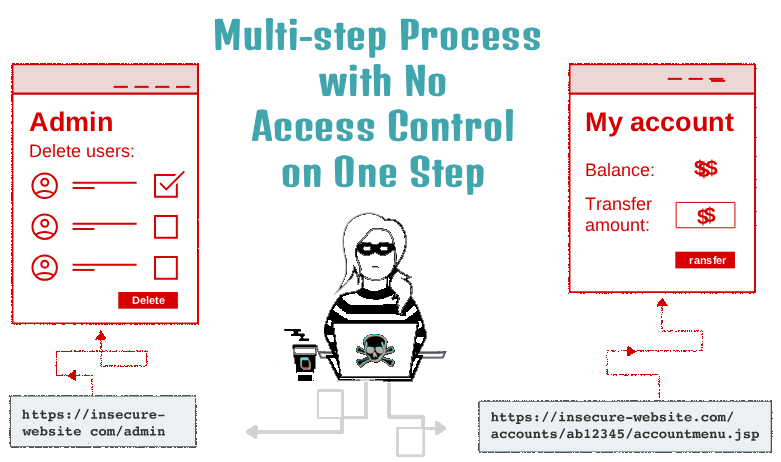
Exploiting broken access control in a multi-step administrative process by replaying the confirmation request with a lower-privileged user's session.
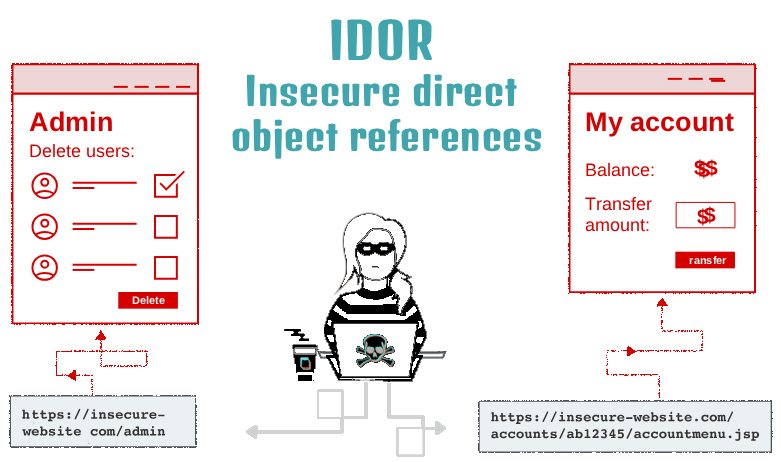
Exploiting an insecure direct object reference in a live chat transcript feature to access another user's conversation and retrieve credentials.
Exploiting broken access control by manipulating a user ID parameter to disclose the administrator's password, access the admin panel, and delete another user.
Exploiting broken access control by modifying a user ID parameter and retrieving another user's API key from a redirect response using Burp Suite.
Exploiting broken access control by modifying a user ID parameter in an authenticated request to retrieve another user's API key.
Testing for broken access control by modifying a user ID parameter and retrieving another user's API key.
Testing how inconsistent HTTP method handling can bypass role-based access controls using Burp Suite Repeater and a low-privileged user session.